Open to 2026 security engineering & research roles

Keyur Aghao

Security Engineer / Vulnerability Researcher

I find the flaws others miss, from a CVSS 9.8 critical CVE to hardware fault-injection and AI-agent security. MS Information Security at Carnegie Mellon, building offensive tooling and defensible research.

Portrait of Keyur Aghao
Now @ CMU
MS Information Security
9.8
CVSS critical CVE, first public PoC
60+
Vulnerabilities disclosed in industry
2×
Microsoft MSRC acknowledgements
1st
MITRE eCTF hardware-security win
3.80
Cumulative QPA at CMU (of 4.0)
About

Breaking things
with rigour.

I'm a master's student in Information Security at Carnegie Mellon University (cumulative QPA 3.80/4.0, graduating Dec 2026), specializing in cyber forensics and incident response. My work spans offensive security, hardware and firmware research, AI-system security, and vulnerability research.

I published the first public proof-of-concept for CVE-2025-20260, a CVSS 9.8 flaw in ClamAV's PDF parser, and was twice acknowledged by Microsoft MSRC for coordinated disclosures. At Bajaj Finserv I uncovered 60+ vulnerabilities across APIs, Active Directory, and cloud infrastructure, authoring PSIRT-grade reports mapped to MITRE ATT&CK.

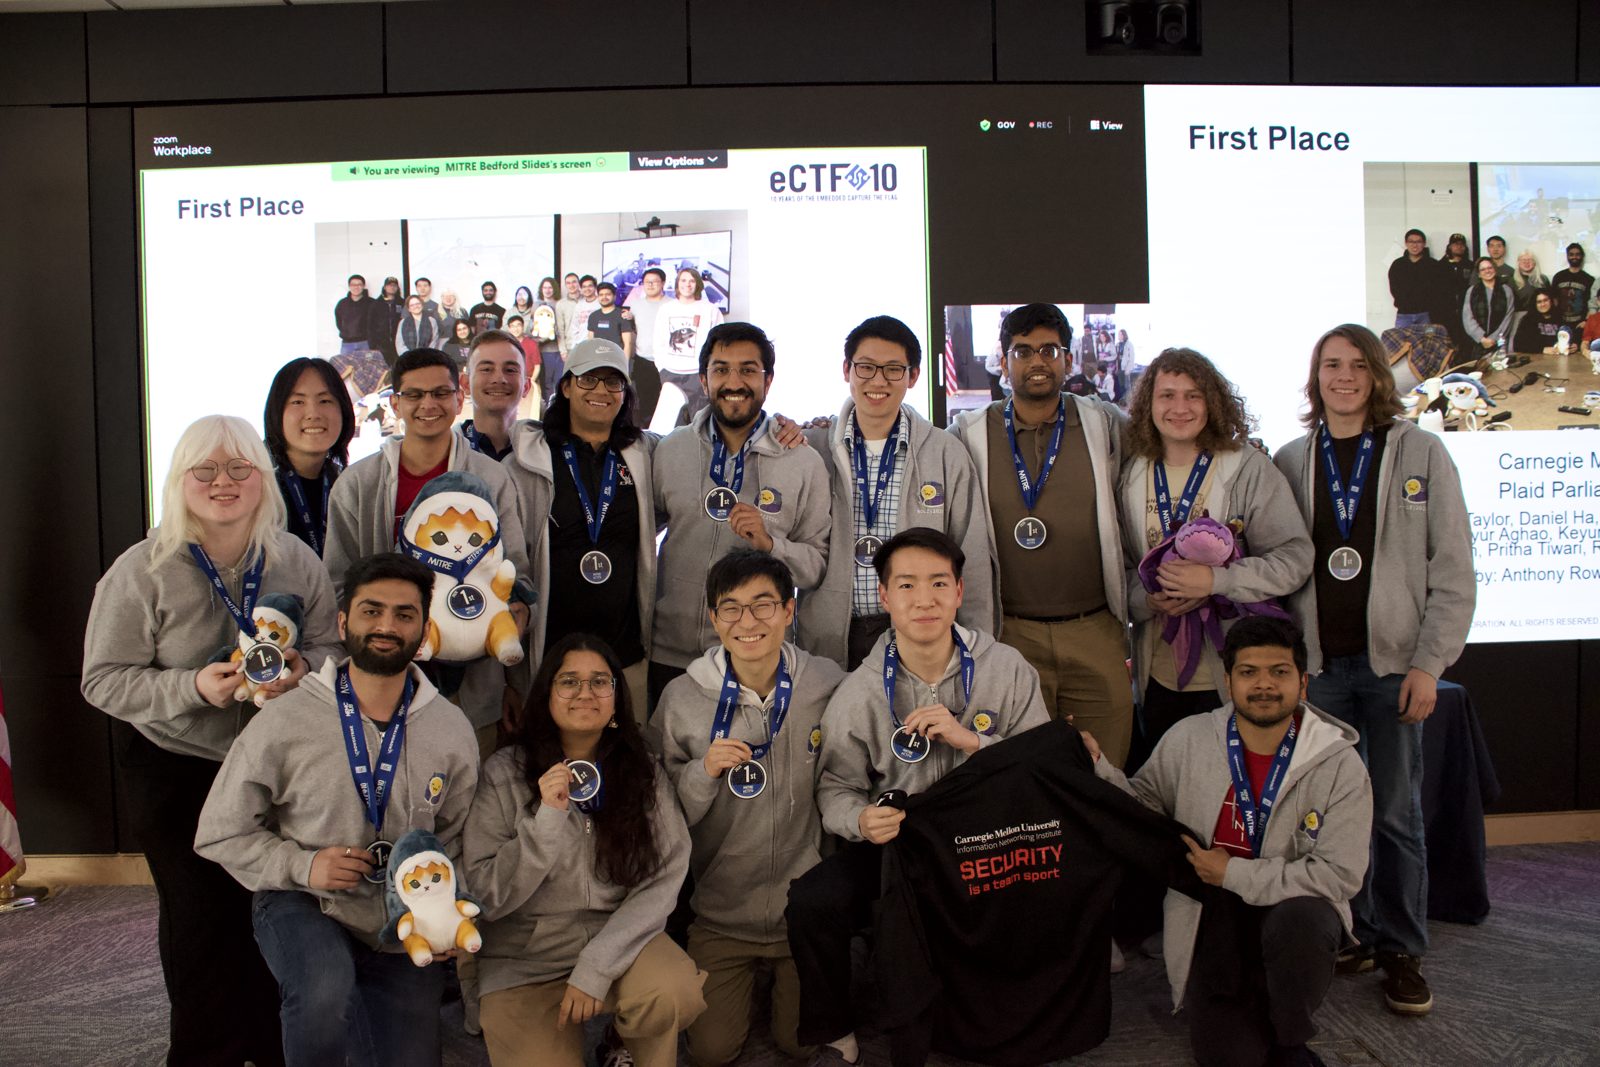
My CMU team took 1st place at MITRE's eCTF embedded-security competition: KiCad PCB design, low-level C firmware, and voltage-glitching fault injection. I'm also a member of Plaid Parliament of Pwning (PPP), CMU's competitive hacking team.

FocusOffensive security, hardware & firmware, AI/LLM security, vuln research
Based inPittsburgh, PA · Carnegie Mellon University
AffiliationsPPP · CyLab · MITRE eCTF
Experience

Where I've worked.

May 2025 – Aug 2025
CMU, CTTEC
Pittsburgh, PA

Enterprise Creation Intern

Deep-Tech Commercialization
  • Supported commercialization of CMU deep-tech research, evaluating startup potential across security, AI and hardware verticals.
  • Conducted market sizing, competitive analysis and IP-landscape assessments for emerging cybersecurity technologies.
May 2024 – Dec 2024
Bajaj Finserv
Pune, India

Red Team Engineer / Domain Manager

Offensive Security · Detection Engineering
  • Discovered 60+ vulnerabilities across APIs, wireless, IoT, web apps, Active Directory and cloud via full-scope penetration testing.
  • Authored PSIRT-grade reports with MITRE ATT&CK mappings, driving an estimated $1M+ in cost savings and a 39% reduction in critical findings.
  • Evaluated 500+ AI/ML models for adversarial robustness; tuned Splunk & QRadar SIEM detections; led Akamai WAF and API-gateway hardening.
Jul 2023 – May 2024
Bajaj Finserv
Pune, India

Software Engineer, Application Security

AppSec · DevSecOps · Incident Response
  • Built and maintained automated tooling for cloud-exposure enumeration and EDR-resilience testing across AWS/Azure/GCP.
  • Integrated SAST and DAST (Semgrep, CodeQL, Burp, ZAP) into CI/CD, shifting security left across 15+ development teams.
  • Performed live incident response, reverse-engineering malicious binaries in IDA Pro and GDB to attribute TTPs and contain breaches.
Jan 2023 – Jul 2023
Bajaj Finserv
Pune, India

API Governance & AppSec Intern

API Security · Automation
  • Assessed 4000+ APIs for OWASP API Top 10 misconfigurations and produced remediation reports for development teams.
  • Published the company-wide API inventory catalog used for compliance audits and faster incident triage.
  • Automated API security scanning with Python and Postman, cutting manual testing time by ~40%.
Selected Work

Things I've built & broken.

Vulnerability Research

CVE-2025-20260

CVSS 9.8 · CriticalCisco ClamAV

The first public proof-of-concept for a critical buffer-overflow in ClamAV's PDF-scanning path, used inside Cisco Secure Email/Web. Published after coordinated disclosure and patch, for defensive research and detection engineering. Documents the vulnerable logic, trigger conditions, the affected/fixed version matrix, and a core-dump analysis of the crash.

Reverse-EngineeringPDF-ParserPSIRTATT&CK-T1562
Offensive Tooling

Mobile Security Research Framework

ReleasedSAST + DAST

A cross-platform Mobile & IoT SAST / DAST / pentest toolkit unifying MobSF, Frida, objection, mitmproxy, nmap and binwalk behind one interface: desktop app, CLI and MCP server over the same engine layer. Bundles 20+ one-click Frida hooks, traffic interception over Wi-Fi/USB/WireGuard, a built-in simulator, and consolidated PDF/HTML/XLSX reporting.

PythonPyQt6FridaMobSFmitmproxy
Digital Forensics

EDB Explorer

Read-onlyMCP server

A cross-platform GUI, CLI and MCP server for forensic database analysis. Opens ESE (ntds.dit, SRUDB, Exchange, WebCache), SQLite, Windows event logs, LevelDB, Access, dBase and SQL/BSON dumps, strictly read-only, with pure-Python parsers, SQL over any format, a cross-database timeline, artifact views for ~60 applications, and signed encrypted project files for hand-over.

PythonPySide6DFIRESE/SQLiteTimeline
RF Sensing · Embedded

wifisense

ESP32 meshSignal processing

Device-free sensing that detects motion and objects using the RF ordinary WiFi hardware already transmits, with no router modification. A single-link RSSI track (validated end-to-end at 82,886 frames / 1041 Hz on real hardware) plus a ~12-node ESP32 mesh for 3D radio-tomographic imaging, sharing one signal-processing and modelling pipeline. Firmware builds for six ESP32 families.

PythonESP32RF-SensingRadio-TomographyML
Recon · Attack Surface

SubHunter

Python + C++AI analysis

An installable CLI for external attack-surface discovery: aggregates subdomains from five OSINT sources, resolves them in parallel with a compiled C++ DNS resolver, optionally runs Nuclei for vulnerability scanning, and delivers a rich terminal report plus a self-contained HTML report, with optional AI-powered security analysis.

PythonC++17OSINTNucleiDNS
Cloud Security · CSPM

Cloud Piercer V2

Multi-cloudSSE dashboard

A multi-cloud tool that discovers publicly reachable object storage across AWS S3, Azure Blob, GCS and DigitalOcean Spaces from a browser dashboard: live scanning with a real-time log stream, concurrent multiprocessing scans, Azure blob enumeration, scheduled recurring scans, and optional AI-based risk classification.

PythonFlaskCSPMAWS/Azure/GCP
Hardware Security · 1st Place

MITRE eCTF, Winning Design

🏆 1st placeFault injection

Took 1st place in MITRE's national embedded-systems security competition. Built a secure embedded design: hardened C firmware with UART/SPI/I2C protocol handling and custom KiCad PCBs, then broke rival designs with voltage-glitching fault injection on ChipWhisperer, bypassing secure-boot signature checks and debug-lock fuses, plus side-channel and protocol-replay analysis.

C-FirmwareKiCadChipWhispererFault-Injection
Firmware RE · CMU Research

DJI Drone Security Evaluation

14 vulns foundResponsible disclosure

A structured security evaluation of the DJI Mavic Mini. Reverse-engineered the DJI DUML protocol over Enhanced Wi-Fi from monitor-mode captures, recovered firmware decryption keys, and performed static analysis of the firmware partitions in Ghidra and binwalk, uncovering 14 vulnerabilities that compose into a full remote unauthenticated root-compromise chain. Findings are in responsible disclosure with the advisor.

Firmware-REGhidraHackRFFrida/LSPosed
Developer Tooling

Code Hierarchy for VS Code

MarketplaceTypeScript

A published VS Code extension: a live function and class hierarchy docked beside your code, with fuzzy subsequence search. It follows the cursor, rebuilds as you type, and falls back to a built-in pattern parser when no language server is available. No sidebar, no clicking around.

TypeScriptVS-Code-APIWebviewLSP
Red Team · Detection Notes

AMSI Evasion Reference

ATT&CK T1562.001Blue-team notes

A catalogued reference of Windows AMSI evasion techniques and the detection gaps they expose. Each entry is annotated with how modern AV/EDR detects or blocks it and mapped to MITRE ATT&CK. Written so blue teams can build detections for the evasion vectors rather than chase individual payloads.

Windows-InternalsDetection-EngineeringEDR
Capabilities

The toolkit.

01 Offensive Security

  • Red Teaming
  • Penetration Testing
  • Exploit Development
  • VAPT
  • Adversary Simulation

02 AI Red Teaming & Security

  • AI Red Teaming
  • LLM Security
  • Prompt Injection
  • Jailbreak Testing
  • Adversarial ML
  • Data Poisoning
  • Model Extraction
  • Guardrails
  • AI Governance

03 AI Security Tooling

  • PyRIT
  • promptfoo
  • garak
  • Rebuff
  • LLM Guard
  • NeMo Guardrails
  • Lakera Guard
  • OWASP LLM Top 10

04 Hardware & Firmware

  • Fault Injection
  • Voltage Glitching
  • ChipWhisperer
  • KiCad PCB
  • UART / SPI / I2C
  • C Firmware

05 Reverse Engineering

  • Ghidra
  • IDA Pro
  • GDB
  • binwalk
  • x86 / x64 Assembly
  • Firmware RE

06 Forensics & Response

  • Digital Forensics
  • Incident Response
  • Threat Hunting
  • Autopsy
  • Mobile Forensics

07 Cloud Security

  • AWS / Azure / GCP
  • CSPM
  • Cloud Exposure
  • Active Directory

08 Application & API Security

  • SAST / DAST
  • API Security
  • Secure SDLC
  • OWASP API Top 10

09 Detection & SIEM

  • Splunk
  • IBM QRadar
  • ELK Stack
  • MITRE ATT&CK
  • IOC Analysis

10 Languages

  • Python
  • C / C++
  • Go
  • PowerShell
  • TypeScript
  • SQL
  • Assembly

11 Offensive Tooling

  • Burp Suite
  • Metasploit
  • Cobalt Strike
  • Nmap
  • Nuclei
  • Wireshark

12 Standards & Frameworks

  • MITRE ATT&CK
  • OWASP (Web / API / LLM)
  • PSIRT Reporting
  • Coordinated Disclosure
  • Threat Modelling
Recognition

Awards & honours.

Winning team at MITRE Embedded Capture-the-Flag
The winning team at MITRE eCTF, Hardware Security Competition
🏆

1st Place, MITRE eCTF

National embedded-systems security competition: secure C firmware and KiCad PCB design, then offensive voltage-glitching fault injection on ChipWhisperer against rival designs.

🥇

First Public PoC, CVE-2025-20260

Published the first public proof-of-concept for a CVSS 9.8 heap-manipulation flaw in Cisco ClamAV's PDF parser.

🛡️

2× Microsoft MSRC Acknowledged

Two independently acknowledged coordinated disclosures: an Azure AD OAuth token race condition and a PowerShell execution-policy bypass.

🎓

Published Researcher & Speaker

Springer book chapter on the Meltdown hardware vulnerability, plus accepted talks at NICE-DT '23, Pulzion '22 and Impetus '23 on micro-architectural attacks.

Publications & Conferences

Research & writing.

2026

Security Evaluation & Reverse Engineering of DJI Drones and Their Protocols

Research paper, Carnegie Mellon University, Information Networking Institute. Advised by Prof. Patrick Tague.
Disclosure in progress
2023

Hardware Vulnerability: Meltdown

Lecture Notes in Networks and Systems, vol. 676. Springer, Singapore.
View publication
2023

Hardware Vulnerability: Meltdown

NIELIT International Conference (NICE-DT '23).
Credentials
2022

Hardware Vulnerability: Spectre

Pulzion '22, by PICT ACM.
Credentials
2023

Hardware Vulnerability: Spectre

Impetus and Concepts 2023.
Credentials
Education

Academic foundation.

Aug 2024 – Dec 2026
Carnegie Mellon University
Pittsburgh, PA · INI

MS, Information Security

Cumulative QPA 3.80 / 4.0 · Cyber Forensics & Incident Response
  • Coursework: Host-Based & Network Forensics, Applied Threat Analysis, Hacking & Offensive Security, Mobile & IoT Security, Security of Networked Systems, Quantum Cryptography & ML Lab.
  • Member: Plaid Parliament of Pwning (PPP), CyLab Security & Privacy Institute, MITRE eCTF team.
Jul 2019 – May 2023
PICT, Pune
Savitribai Phule Pune University

BE, Computer Engineering

GPA 3.89 / 4.0 · Springer Publication (2023)
  • Coursework: Computer Networks, Operating Systems, Cryptography, Database Management, Algorithm Design.
Credentials

Licenses & certifications.

Professional

OSCP In progressOffensive Security · 2025
Certified Ethical Hacker (CEHv11)EC-Council · 2021
Certified Network Defender (CND)EC-Council · 2021
Cryptography & Network SecurityIIT Kharagpur · 2022
Network Security & Cyber ForensicsNITTTR · 2022

Applied & Coursework

Jr Penetration TesterTryHackMe · 2024
Penetration TestingUdemy · 2021
Python 3 MasterclassUdemy · 2021
Cyber Security (AICTE)NITTTR · 2020
Get in touch

Let's build something secure.

Whether you're hiring a security engineer, want to discuss research, or just want to talk shop, my inbox is always open.

kaghao@andrew.cmu.edu